






For international ecommerce brands, compliance is not merely an operational checkbox—it is a prerequisite for business survival. Over the past three years, marketplace gatekeepers and international privacy regulators have drastically intensified scrutiny over merchant-to-buyer communications.
A single non-compliant outreach on Amazon can trigger immediate account suspension, while GDPR violations for improper personal data retention carry catastrophic financial fines.
This guide provides ecommerce operators with a clear framework for building compliant, automated customer service operations using Solvea.
Marketplace Messaging Restrictions
1. Amazon Buyer-Seller Messaging Rules
Amazon enforces strict boundaries on seller-initiated communication:
- No Marketing Content: Links to external DTC stores, coupon codes, and social media handles are immediately flagged.
- Review Request Restrictions: Sellers must use the official "Request a Review" protocol and are forbidden from offering incentives for positive feedback.
- Frequency Limits: Only one post-order follow-up is allowed per transaction.
2. DTC Messaging Regulations (TCPA & CAN-SPAM)
For Shopify DTC operations utilizing SMS and email notifications:
- Prior Express Consent: Sending promotional SMS requires auditable double opt-in consent records.
- Mandatory Opt-Out: Every message must include a frictionless "STOP" mechanism.
- Quiet Hours Enforcement: Prohibits automated communications between 9:00 PM and 8:00 AM in the recipient's local time zone.
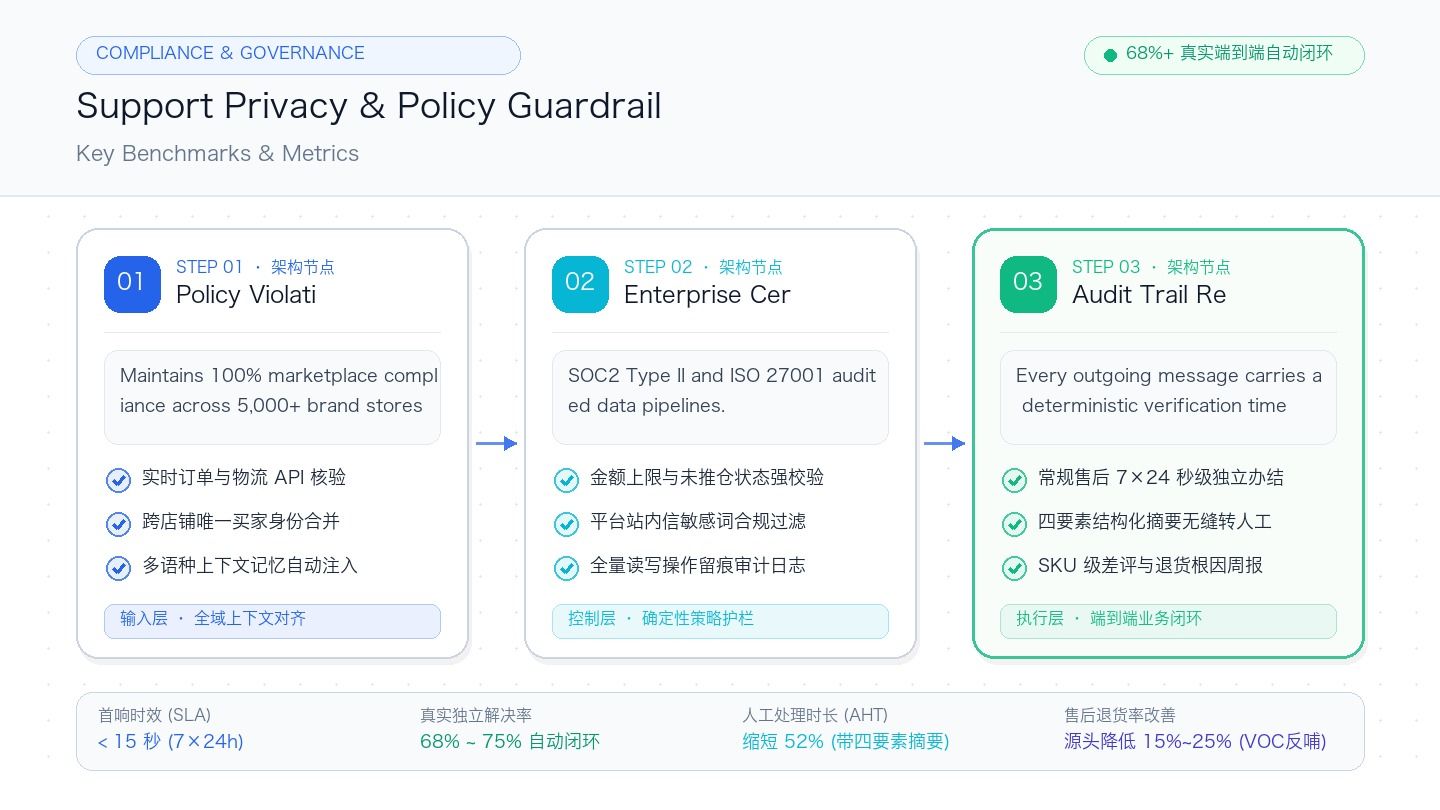
Privacy Governance: GDPR & CCPA in Customer Support
Support logs frequently contain sensitive personally identifiable information (PII)—including physical addresses, phone numbers, and payment details.
1. Dynamic Data Masking (Data Minimization)
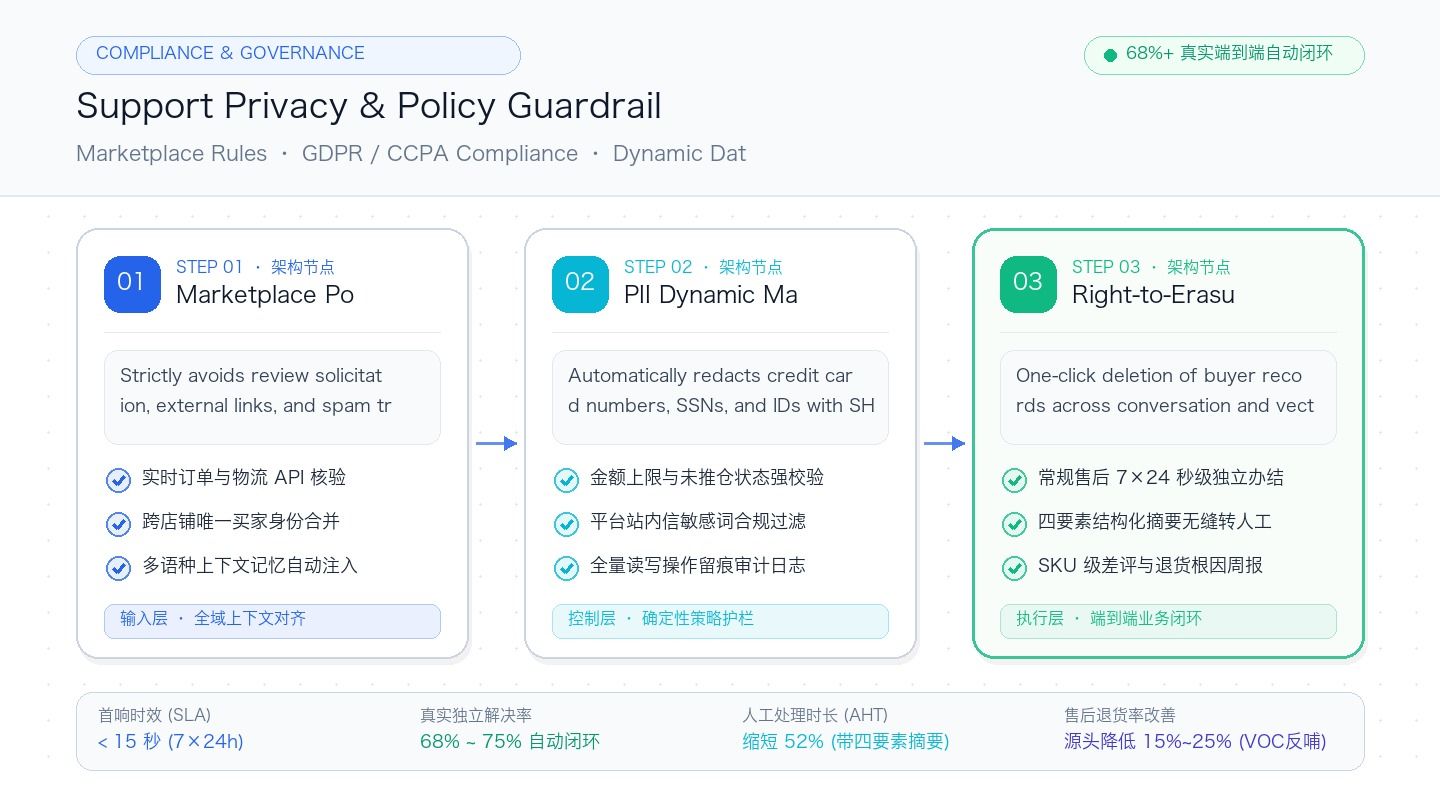
Solvea routes all incoming customer interactions through an automated sanitization sandbox. Credit card numbers, personal identification documents, and sensitive credentials are encrypted and masked before entering model inference pools, preventing accidental data leaks.
2. Operationalizing the Right to Erasure
Under GDPR Article 17, European consumers have the legal right to demand the total deletion of their personal data. Solvea enables one-click data erasure across active tickets, cold archives, and vector database embeddings.
Conclusion
Protecting your brand's standing on major marketplaces and complying with global privacy laws requires engineering guardrails rather than human diligence alone. Explore how Solvea keeps your communication 100% compliant.
---
Related Benchmarks & Official Resources
- 📊 TCO & Pricing Guide: After-Hours Support Pricing: Staffing vs. AI Cost Benchmarks
- 📈 Revenue Impact Study: The Revenue Cost of Missed Inquiries Outside Business Hours
- 🚀 Product Overview: Solvea Autonomous CX Platform for Global Ecommerce
- 🤝 Consultation & Demo: Request a Personalized Solvea Demo & Support Audit